Wednesday, 18 November 2026, story 5 of 7
GitHub and Microsoft pilot sends maintainers 99 verified AI reports
Of thousands of AI findings across six projects, maintainers had fixed 55 by November 15, GitHub says, and 14 of those fixes were in a release.
What happened
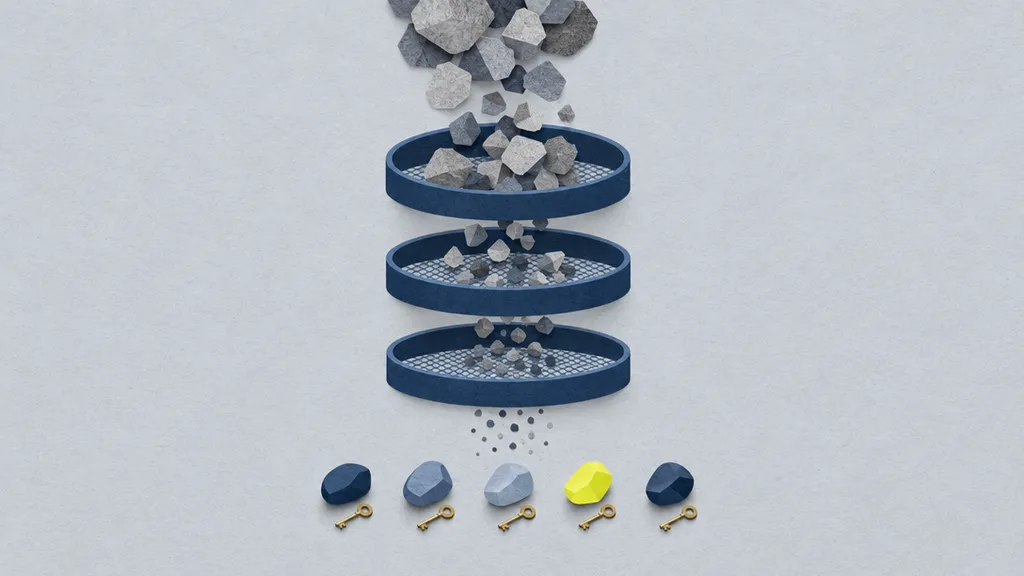
GitHub and Microsoft say a pilot of Microsoft's Codename MDASH scanner turned thousands of possible vulnerabilities into 99 private reports for six open source projects. An AI triage agent removed duplicates and invalid findings, and seven Microsoft FORGE Lab researchers checked the rest by hand. Each report came with a proof of concept and a suggested fix.
As of November 15, maintainers had fixed 55 reports, GitHub says, and 14 of those fixes were in a release. Caddy's maintainers fixed all 22 of their reports in a week or less. The pilot ran on the earlier MAI Cyber model.
What it means
Scanning was the cheap part. By GitHub's account, what made the reports usable was the human work around it: about two days of hand review per project by seven researchers. GitHub says that work does not scale yet, so the jump from thousands of findings to 99 reports says as much about the filter as about the model.
The evidence is thin. Six projects is a small sample, all are alumni of GitHub's Secure Open Source Fund, the quotes are ones maintainers chose to share, and the fix counts come from GitHub. The standard it sets for senders is still concrete: verify, report privately, attach a fix. Watch whether the promised scans for fund alumni keep that review quality. The source does not say whether MDASH will be available beyond the pilot, or at what price.
What to do: Before sending AI-found vulnerabilities to a project, verify each one and attach a fix; maintainers should switch on private vulnerability reporting.
Source
Filed under Safety and security. Published .
"What it means" is analysis, not reporting. Found an error? Write to daily@vibitely.com.